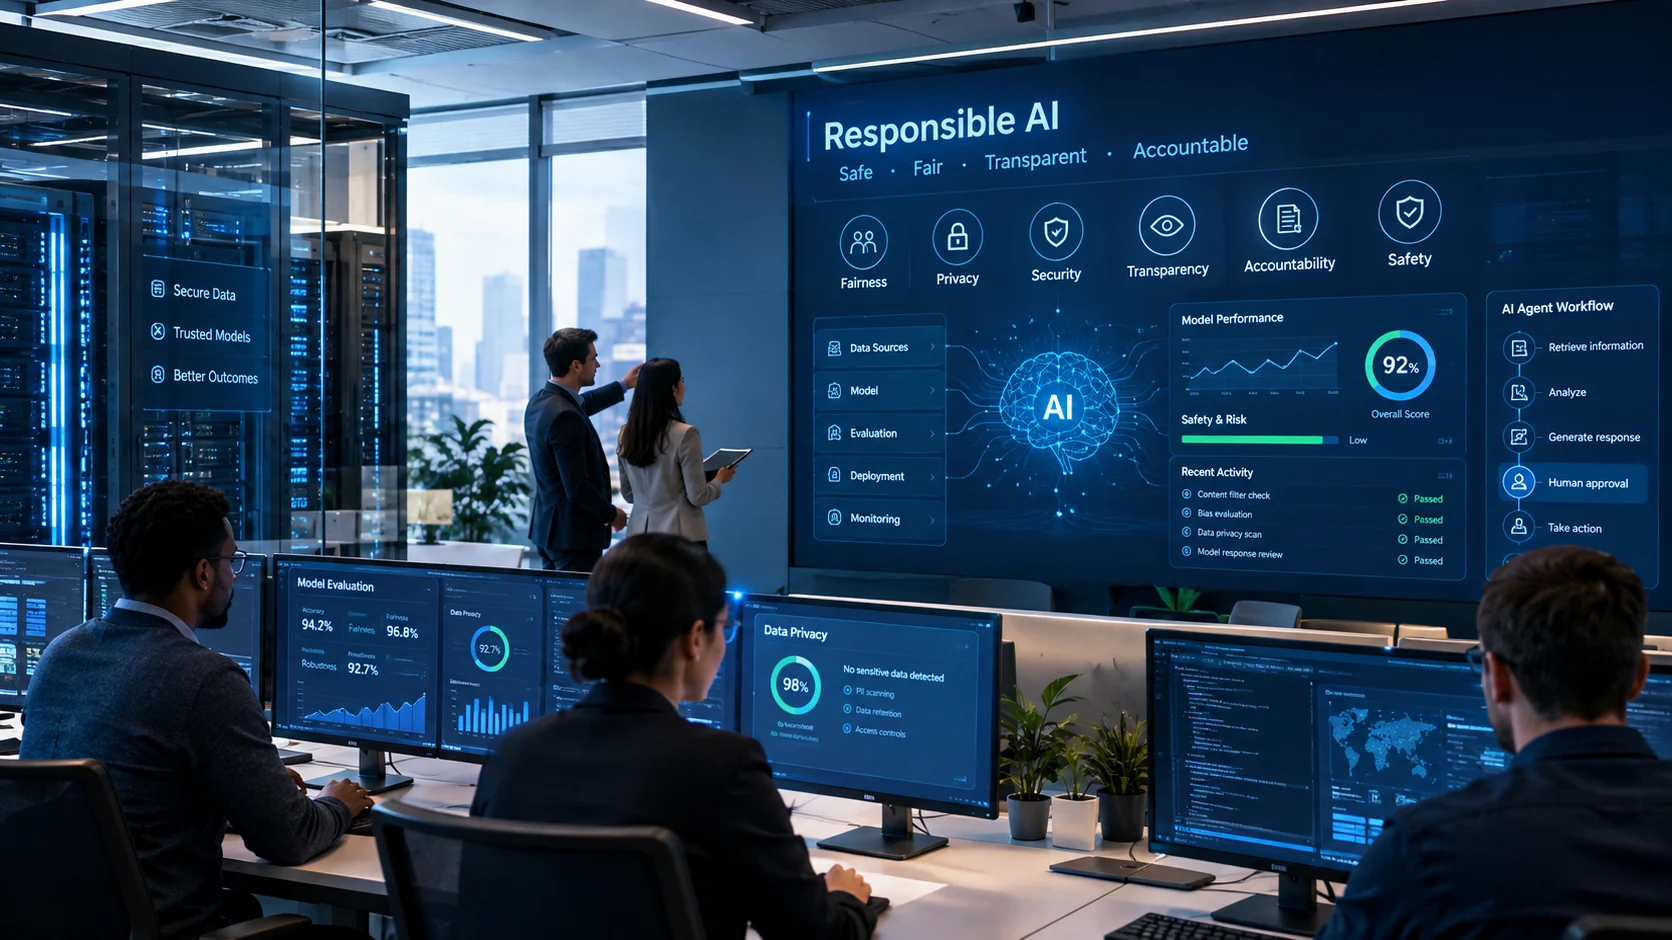
Responsible AI is the practice of designing, developing, deploying, and monitoring AI systems so they are safe, fair, transparent, privacy-conscious, accountable, and aligned with human goals. It turns broad principles such as fairness and safety into practical controls across the AI lifecycle, from data and model development to deployment and ongoing monitoring.
Responsible AI at a Glance
- Responsible AI is a lifecycle practice, not a final ethics review before launch.
- Core concerns include fairness, safety, privacy, security, transparency, inclusiveness, and accountability.
- NIST AI RMF, ISO/IEC 42001, and the OECD AI Principles provide important governance reference points.
- Generative AI and AI agents introduce additional risks, including hallucinations, prompt injection, data leakage, misuse, and excessive autonomy.
- Compliance is only one part of responsible AI. A system can meet a regulatory requirement and still create operational or societal risks.
- Effective programs combine technical testing, governance, human oversight, documentation, monitoring, and clear ownership.
What Is Responsible AI?
Responsible AI is an approach to building and using artificial intelligence in ways that manage potential harms while preserving useful outcomes.
It covers the complete AI lifecycle. That includes defining the use case, collecting and preparing data, selecting or developing models, testing performance, deploying the system, monitoring real-world behavior, and eventually modifying or retiring it.
The term does not describe one technology or software product. It describes a set of engineering, governance, risk-management, and organizational practices.
Different organizations use slightly different terminology. Microsoft, for example, organizes its responsible AI approach around fairness, reliability and safety, privacy and security, inclusiveness, transparency, and accountability. Google’s responsible AI guidance similarly emphasizes areas such as fairness, accountability, safety, and privacy.
The broader goal is straightforward: AI systems should create useful outcomes without exposing people or organizations to unmanaged risks that could reasonably have been identified and addressed.
Why Does Responsible AI Matter?
AI systems increasingly influence decisions, content, recommendations, workflows, and automated actions.
A conventional software bug might cause an application to crash. An AI failure can be less obvious. A model might produce a convincing but incorrect answer, behave differently across demographic groups, expose sensitive information, or make an inappropriate recommendation while appearing confident.
Generative AI increases the challenge because large language models can produce fluent output without guaranteeing that the output is factually correct.
AI agents add another layer. Instead of simply generating text, an agent may access tools, retrieve information, execute workflows, or take actions on a user’s behalf.
That makes responsible AI increasingly important for both model developers and organizations deploying third-party AI systems.
The Core Principles of Responsible AI
There is no single universal checklist used by every organization. However, several principles consistently appear across major responsible AI frameworks.
1. Fairness
AI should not systematically produce unjustified disadvantages for particular groups.
Fairness is not simply a matter of removing sensitive attributes from a dataset. Other variables can act as proxies, and apparently neutral systems can produce different outcomes across populations.
Testing should therefore consider the specific context, affected groups, intended use, and potential consequences.
For high-impact applications, organizations may need formal fairness assessments rather than relying on general-purpose model benchmarks.
2. Reliability and Safety
AI systems should behave consistently within their intended operating conditions and fail safely when those conditions are exceeded.
For generative AI, this can involve testing for hallucinations, unsafe outputs, prompt injection, jailbreaks, and inappropriate tool use.
For AI agents, reliability also includes controlling what actions the system can perform and when human approval is required.
3. Privacy and Security
Responsible AI requires more than protecting the model itself.
Organizations should consider the entire information flow:
- What data enters the system?
- Where is that data stored?
- Who can access it?
- Is it used for training or model improvement?
- How long is it retained?
- Can users request deletion?
- Can prompts or retrieved documents expose confidential information?
- What happens when a connected AI agent accesses another system?
Privacy and security controls should match the sensitivity of the application.
4. Transparency and Explainability
People should have enough information to understand when and how AI is being used, particularly when its output can materially affect them.
Transparency does not necessarily mean revealing model weights or exposing every internal calculation.
It can instead involve clear documentation of:
- The system’s intended purpose
- Known limitations
- Data sources
- Major risks
- Human oversight
- Evaluation methods
- Appropriate and inappropriate uses
Explainability is especially important when an AI system contributes to consequential decisions.
5. Accountability
Someone must ultimately be responsible for an AI system’s behavior and impact.
That responsibility should not disappear behind phrases such as “the model decided.”
Effective governance assigns ownership across product, engineering, security, legal, compliance, and business teams according to the system’s risk.
Accountability also requires traceability. Teams need sufficient records to investigate incidents, understand changes, and determine why a system behaved differently over time.
6. Inclusiveness
Responsible AI should account for people with different languages, abilities, backgrounds, and circumstances.
A model that performs well for the majority population may still fail badly for underrepresented users.
Accessibility and multilingual performance can therefore be responsible AI concerns, not merely product-quality improvements.
How Responsible AI Works in Practice
Responsible AI becomes useful when principles are translated into operational controls.
A practical lifecycle looks like this:
1. Define the use case
Start by documenting what the AI system is supposed to do and what it must not do.
2. Assess risk
Identify affected users, potential harms, sensitive data, misuse scenarios, and consequences of failure.
3. Select data and models
Evaluate data quality, provenance, representativeness, licensing, privacy requirements, and model limitations.
4. Test before deployment
Evaluate accuracy, robustness, fairness, security, safety, privacy, and domain-specific failure modes.
5. Establish human oversight
Decide which decisions require review and when the AI must defer to a person.
6. Deploy with controls
Use access restrictions, logging, monitoring, content safeguards, rate limits, and other controls appropriate to the application.
7. Monitor continuously
AI systems can change as models, prompts, data, users, integrations, and regulations change.
8. Respond and improve
Investigate incidents, update safeguards, retrain or replace models when necessary, and document significant changes.
This lifecycle approach aligns with the broader risk-management philosophy of NIST’s AI RMF, which is designed to help organizations manage AI risks throughout development and use.
Responsible AI and Generative AI
Generative AI creates distinctive responsible AI challenges because models generate new content rather than simply classifying existing information.
Common risks include:
- Hallucinated facts
- Copyright and intellectual-property concerns
- Sensitive-data leakage
- Prompt injection
- Jailbreaking
- Biased or harmful outputs
- Synthetic misinformation
- Inadequate disclosure of AI-generated content
- Overreliance on fluent but incorrect responses
NIST’s Generative AI Profile extends its AI Risk Management Framework specifically for generative AI and identifies risks and corresponding actions organizations can consider when managing them.
For organizations using large language models, responsible AI should therefore extend beyond model selection.
A reliable implementation may combine retrieval-augmented generation (RAG), access controls, source attribution, output evaluation, moderation, human review, and monitoring.
RAG can reduce some factual errors by grounding responses in approved information, but it does not automatically make a system accurate or responsible. Poor retrieval, outdated documents, malicious content, or weak access controls can still produce failures.
Responsible AI for AI Agents
AI agents raise the stakes because they can perform actions rather than merely provide information.
An agent might read email, query databases, create tickets, update records, call APIs, or execute business workflows.
Responsible deployment therefore requires explicit boundaries.
Important controls for AI agents
- Least-privilege access: Give the agent only the permissions it needs.
- Human approval: Require confirmation for high-impact or irreversible actions.
- Tool restrictions: Limit which APIs and applications the agent can access.
- Audit logs: Record important actions and decisions.
- Escalation: Route ambiguous or sensitive cases to humans.
- Prompt-injection defenses: Treat external content as potentially untrusted.
- Continuous testing: Test realistic misuse and failure scenarios.
Microsoft’s current responsible AI guidance specifically recommends making architectural decisions about grounding, access boundaries, human approval, and agent limits early in development rather than treating responsible AI as a final review.
Responsible AI Frameworks and Standards
Several frameworks can help organizations turn responsible AI principles into repeatable processes.
| Framework / Standard | Primary Purpose | Best Fit | Important Limitation |
|---|---|---|---|
| NIST AI RMF | AI risk management | Organizations building or deploying AI | Voluntary framework |
| NIST GenAI Profile | Generative AI risk management | LLM and generative AI deployments | Guidance rather than a universal certification |
| ISO/IEC 42001 | AI management system | Organizations seeking structured AI governance | Management-system standard, not a guarantee that individual models are safe |
| OECD AI Principles | International principles for trustworthy AI | Policy and organizational strategy | High-level principles require operationalization |
| EU AI Act | Legal requirements for AI in the EU | Organizations within its scope | Obligations depend on system, role, and use case |
NIST describes its AI RMF as voluntary and designed to help organizations manage AI risks while promoting trustworthy and responsible development and use.
ISO/IEC 42001 is different in character. It specifies requirements for establishing, implementing, maintaining, and continually improving an Artificial Intelligence Management System within an organization.
The OECD AI Principles provide another international reference point, covering areas including human rights, fairness, privacy, transparency, robustness, security, safety, and accountability. The principles were updated in 2024 to address developments such as generative AI.
These frameworks can complement one another. They should not be treated as interchangeable certifications or as proof that an AI system is automatically safe.
Responsible AI and the EU AI Act
Responsible AI and AI regulation overlap, but they are not identical.
The EU AI Act provides legally binding requirements for organizations within its scope, while responsible AI is a broader governance and engineering concept.
As of September 2026, the EU AI Act has entered its broader application phase, although different requirements have different effective dates. Certain prohibited practices and AI literacy requirements began applying earlier, while requirements for some high-risk systems have later transition dates.
On 2 August 2026, new transparency requirements began applying, including requirements concerning certain AI interactions and AI-generated or manipulated content.
This matters because organizations should not reduce responsible AI to “AI Act compliance.”
Regulation establishes legal obligations. Responsible AI also asks whether the system is appropriate for its purpose, technically robust, understandable to users, and adequately governed.
Responsible AI vs. AI Ethics
The terms are related but not identical.
AI ethics focuses heavily on questions about values, rights, fairness, human dignity, and acceptable uses of AI.
Responsible AI translates many of those concerns into concrete organizational and technical practices.
For example:
Ethical question: Should an AI system be used for this purpose?
Responsible AI question: If it is used, what controls, testing, oversight, documentation, and monitoring are necessary?
Strong AI programs need both.
Common Responsible AI Mistakes
Treating responsible AI as a one-time review
AI systems change after launch. New data, model updates, integrations, prompts, and user behavior can create new risks.
Responsible AI should therefore be continuous.
Assuming a famous model is automatically safe
A capable foundation model can still be inappropriate for a specific application.
The deployment context matters.
Confusing benchmark performance with real-world reliability
A model can perform strongly on standardized benchmarks while failing in a company’s actual workflow.
Organizations should evaluate systems against realistic tasks and failure conditions.
Assuming privacy claims without checking contracts
Statements such as “enterprise data is private” can conceal important distinctions.
Organizations should review actual terms governing data retention, training use, logging, subprocessors, regional processing, and administrative access.
Treating compliance as proof of safety
A certification, audit, or regulatory compliance statement does not eliminate every AI risk.
For example, SOC 2 is not synonymous with zero data retention. Organizations must examine the specific service’s data-handling terms rather than infer retention practices from a security certification.
Giving AI excessive autonomy
The more consequential an AI system’s actions are, the more important permission boundaries and human escalation become.
An AI assistant that drafts an email and an AI agent that transfers funds should not operate under the same governance model.
How to Build a Responsible AI Program
Organizations do not need to begin with a massive governance department.
A practical starting point is a documented AI inventory.
For every AI application, record:
- Purpose: What does the system do?
- Owner: Who is accountable?
- Users: Who interacts with it?
- Data: What information does it process?
- Model: Which model or provider does it use?
- Risk: What happens if it fails?
- Controls: What safeguards exist?
- Oversight: When does a human intervene?
- Monitoring: What signals indicate failure?
- Change management: How are updates reviewed?
Organizations can then assign risk tiers.
A low-risk internal writing assistant might require lightweight documentation and security review.
A system involved in employment, healthcare, financial decisions, critical infrastructure, or other sensitive activities may require substantially stronger evaluation, governance, and legal review.
The OECD’s 2026 Due Diligence Guidance for Responsible AI similarly frames responsible AI as an ongoing due-diligence process rather than a one-time declaration.
What Should Developers Evaluate?
For developers, responsible AI becomes much more concrete when converted into engineering tests.
Depending on the system, teams may evaluate:
- Accuracy and groundedness
- Hallucination rates
- Toxic or harmful outputs
- Bias across relevant groups
- Prompt-injection resistance
- Unauthorized information disclosure
- Tool-use behavior
- Access-control failures
- Robustness to adversarial inputs
- Performance degradation
- Human override mechanisms
- Logging and auditability
For LLM applications, testing should cover both the model and the surrounding application.
A responsible AI review that tests only the base model can miss vulnerabilities introduced by RAG pipelines, prompts, plugins, APIs, databases, or agent tools.
Who Needs Responsible AI?
Responsible AI applies to more than large technology companies.
Businesses
Businesses need governance when employees or customer-facing systems use AI for important workflows.
Developers
Developers need practical controls for testing, security, privacy, evaluation, and deployment.
AI Researchers
Researchers may need reproducible evaluations, documentation, dataset analysis, and transparent reporting of limitations.
Marketers and Content Teams
Teams using generative AI should consider disclosure, factual accuracy, copyright, brand safety, and human editorial review.
Executives and Risk Teams
Leaders need visibility into which AI systems exist, who owns them, what risks they introduce, and how those risks are managed.
What Matters Most When Evaluating an AI System?
A useful responsible AI assessment should go beyond asking, “Which model is most capable?”
Instead, ask:
- Is the system appropriate for the intended use?
- What data does it receive?
- Where does that data go?
- What can the model access?
- What can it actually do?
- How is performance evaluated?
- What happens when it is wrong?
- Can a human intervene?
- Are important actions logged?
- How are incidents handled?
- How does the provider handle retention and training data?
- What happens if the vendor changes the model or pricing?
- Can the organization migrate to another provider?
This last group of questions highlights an often-overlooked issue: responsible AI is also a procurement and architecture problem.
Vendor lock-in, opaque model updates, API dependency, changing usage limits, and insufficient documentation can create operational risk even when a model performs well.
The Future of Responsible AI
The field is moving from principles toward operational governance.
That shift is visible in the increasing use of AI management systems, risk frameworks, model evaluations, transparency reporting, and lifecycle monitoring.
It is also becoming more important as AI systems become multimodal and agentic.
Google’s 2026 Responsible AI Progress Report describes a lifecycle approach spanning research, model development, deployment, and post-launch monitoring. Microsoft’s 2026 transparency reporting similarly emphasizes governance that evolves as generative and agentic AI capabilities expand.
The next phase of responsible AI is therefore less about publishing principles and more about proving that those principles influence engineering decisions.
That means measurable controls, documented ownership, repeatable evaluations, meaningful human oversight, and evidence that safeguards continue working after deployment.
Frequently Asked Questions
What is responsible AI?
Responsible AI is the practice of designing, developing, deploying, and monitoring AI systems in ways that manage risks and support safe, fair, transparent, privacy-conscious, and accountable outcomes.
What are the main principles of responsible AI?
Common principles include fairness, reliability and safety, privacy and security, transparency, accountability, and inclusiveness. Different frameworks use different terminology and group these concepts differently.
Why is responsible AI important for generative AI?
Generative AI can produce convincing but incorrect or harmful content and can introduce risks involving privacy, security, bias, intellectual property, and misuse. Responsible AI provides processes for identifying, testing, mitigating, and monitoring those risks.
Is responsible AI the same as AI compliance?
No. AI compliance focuses on meeting applicable laws, regulations, contracts, or standards. Responsible AI is broader and also covers engineering practices, risk management, human oversight, product decisions, and ongoing monitoring.
How can a company start implementing responsible AI?
A company can start by creating an inventory of its AI systems, assigning accountable owners, assessing risks, documenting data and model usage, defining human-oversight requirements, testing important failure modes, and monitoring systems after deployment.
Conclusion
Responsible AI is best understood as a practical discipline for managing the risks and impacts of AI throughout its lifecycle.
For organizations, the important question is not simply whether an AI model is powerful. It is whether the complete system is appropriate for its purpose, protects sensitive information, behaves reliably, treats affected people fairly, provides meaningful transparency, and has accountable human oversight.
Frameworks such as NIST AI RMF, ISO/IEC 42001, and the OECD AI Principles can provide useful foundations, while applicable laws such as the EU AI Act introduce additional obligations.
The strongest approach is therefore contextual. Evaluate the use case, data, model, integrations, permissions, users, consequences, and operating environment before deciding what responsible AI controls are necessary.
Alex Smith is an AI-focused tech writer at Aixorbit.com, sharing simple and actionable insights on artificial intelligence, automation and digital growth.